
Access Control, Intrusion Detection and Security Posts under GEBSS
Access control is often treated as a door-security project.
A reader is installed, a lock is fitted, cards are issued and the door is considered secure.
The Guidelines for Enhancing Building Security in Singapore (GEBSS) takes a much wider view.
Access control needs to work together with:
the physical door, automatic closing, intrusion detection, surveillance, security personnel, security procedures and response.
GEBSS defines access control as determining who may enter particular areas or access particular assets. It also says the access-control system should be designed together with the building’s other security systems.
Likewise, an intrusion alarm does little if the alarm cannot be identified or nobody responds to it. A security guard is less effective if the guard post has blind spots or itself becomes an easy route into the building.
The useful design question is therefore:
How do we control authorised access, detect unauthorised entry and enable security personnel to respond effectively?
What does GEBSS mean by access control?
GEBSS describes access control as the ability to decide who may or may not enter specific areas or access particular assets.
Its key considerations include:
- minimising entrances;
- deciding which areas should have restricted access;
- ensuring security measures do not interfere with fire protection and safety; and
- maintaining access for persons with disabilities.
The access-management plan should first identify what areas and assets require protection, after which suitable controls can be selected.
This is important because GEBSS does not begin with:
“How many card readers do we need?”
It begins with:
“Which areas and assets actually require controlled access?”
Does every door need electronic access control?
GEBSS does not say that every door in a building requires a card reader.
It says that external doors regularly used by authorised persons only require access control and that the designer should first determine which areas and assets need access restriction.
So the required security level should reflect:
the location of the door, who uses it, what it protects and the consequences if unauthorised access occurs.
A general office door and an entrance to a Critical Asset do not necessarily require the same treatment.
What components make up an access-control system?
GEBSS makes the useful point that access control is a combination of physical elements and security procedures, not simply a reader.
It lists components such as:
card readers, door-control panels, electromagnetic and electric locks, emergency escape break-glass devices, door-position detectors, access-control software, operator stations and automatic door-closing mechanisms.
Consultant’s perspective
This means a door should be treated as a complete controlled opening.
For example, an expensive reader adds little security if:
the door does not close properly, the lock does not secure correctly, the door position is not monitored or the surrounding construction can easily be bypassed.
Does GEBSS require door closers on access-controlled doors?
GEBSS states that all access-controlled doors should be equipped with an automatic door-closing mechanism.
This makes operational sense because an access-controlled door cannot reliably control access if it remains open after an authorised user passes through.
Consultant’s perspective
When reviewing an access-control system, it is therefore useful to test more than credential acceptance.
The assessment should also verify that the door:
closes fully, latches correctly and returns to its secured condition after use.
What does GEBSS say about emergency exit doors?
GEBSS gives emergency exits particular attention.
In its building-design discussion, it says every emergency exit door should have a detector connected to an alarm system so that unauthorised opening generates an alert.
The locking arrangement must also be appropriate for an emergency door and comply with applicable regulations and standards.
This illustrates the two objectives that have to coexist:
Prevent misuse of the emergency exit while preserving safe emergency egress.
Can security override fire and life-safety requirements?
No.
GEBSS expressly says access-control measures should not interfere with fire protection and safety systems.
Its regulatory section goes further and states that applicable Singapore building codes, regulatory controls and standards must be followed, and where there is a contradiction between GEBSS and the building code, the building code prevails.
That is an important limitation when interpreting security recommendations concerning:
locks, doors, gates and emergency exits.
Security cannot be designed independently of life safety.
What does “fail-secure” mean in the GEBSS access-control section?
GEBSS says that a door intended to provide forced-entry protection should use an electric lock that is fail-secure. It also says main entrance doors should have an automatic locking mechanism that allows external guards to lock the doors if an emergency occurs outside.
However, that statement should not be interpreted as permission to ignore fire-safety requirements.
The same GEBSS access-control section specifically requires security measures not to interfere with fire and safety systems, and its regulatory section says governing codes take precedence.
Consultant’s perspective
The locking philosophy therefore needs to be determined door by door, taking into account both:
security requirements
and
the applicable emergency-egress and fire requirements.
Does GEBSS require biometrics?
No universal biometric requirement should be inferred from GEBSS.
In its Layered Protection Concept, GEBSS gives both biometric and card-access systems as examples of ways to verify identity and support the Deny layer.
The appropriate authentication method should therefore follow the security requirement of the protected area rather than assuming biometrics are automatically necessary.
What is the role of intrusion detection?
Access control manages normal authorised movement.
An Intrusion Detection System (IDS) is intended to detect an event that may indicate unlawful or abnormal entry.
GEBSS says IDS can monitor events such as:
doors or windows opening, crossing defined lines, movement within an area, and even changes in environmental conditions depending on the detection technology. A typical IDS can include detectors, control equipment, displays, communications devices, sirens and backup batteries.
The IDS therefore supports the Detect layer in GEBSS’s Defence-in-Depth model.
Is access control the same as intrusion detection?
No.
The two systems can overlap, but they perform different primary functions.
Access control determines whether someone should be allowed through a controlled point.
Intrusion detection identifies activity indicating that a protected boundary or area may have been breached.
For example:
A valid card presented at a door is primarily an access-control event.
A forced opening of that door without authorisation is an intrusion event.
GEBSS specifically expects access control and other security systems to be designed together rather than in isolation.
What types of intrusion detectors does GEBSS discuss?
GEBSS describes several types of detector technology.
For indoor applications, examples include:
balanced magnetic switches, glass-break detectors and passive infrared detectors.
For outdoor applications, examples include:
active infrared and microwave detectors.
It also discusses technologies that can operate in different environments, such as infrared beams, step detectors, video motion detection and several types of fence-line intrusion detection.
The important point is that different sensors detect different forms of intrusion.
There is no single detector suitable for every situation.
How should the correct intrusion detector be selected?
GEBSS says detector selection should take account of:
the installation location and environmental conditions, including whether the detector is indoors or outdoors and factors such as humidity and temperature.
This is significant because sensor performance can depend heavily on its environment.
Consultant’s perspective
The question should therefore not simply be:
“Which motion detector is best?”
It should be:
“What intrusion behaviour are we trying to detect, where will the detector be installed and what environmental conditions could affect it?”
Why are false alarms important?
GEBSS specifically warns against detectors with a high false-alarm rate.
Its concern is simple:
If false alarms occur too frequently, a genuine alarm may eventually be ignored.
It therefore recommends suitable calibration and says the display should clearly identify the zone and detector that generated the event.
False-alarm management is therefore a security issue, not merely an inconvenience.
Should all intrusion detectors operate the same way?
No.
GEBSS distinguishes between two broad detector arrangements.
24-hour detectors are intended for openings that should normally remain permanently closed, such as emergency exits.
Day/night detectors can be used at doors that legitimately operate during the day but should be secured during after-hours periods.
GEBSS notes that separating these detector types allows the system to prioritise outputs more effectively.
Does this mean emergency exit alarms should remain active all the time?
GEBSS specifically places emergency exits in its example of 24-hour detection, meaning those openings are expected to be continuously monitored because they are normally intended to remain closed.
This aligns with the earlier GEBSS statement that emergency exit doors should be connected to an alarm system to detect unauthorised opening.
Should daytime and after-hours alarms behave differently?
GEBSS allows for that concept.
It discusses different alarm outputs for different operational conditions, giving an example of a buzzer during the day and a siren at night.
The wider principle is that intrusion detection should reflect how the building actually operates.
A door that opens hundreds of times during business hours has a very different normal pattern from that same door opening at 3:00 am.
Should an intrusion alarm automatically notify someone?
GEBSS says the system should include means to alert response forces in the event of a breach and that sirens or other alarm elements should be considered.
The important point is that detection has to lead to response.
An alarm stored only in an event log may technically detect the incident but may not provide an effective security outcome if nobody acts on it.
Are magnetic door contacts enough to detect forced entry?
Not always.
GEBSS says magnetic or mechanical switches are effective for detecting the unauthorised opening of doors and windows.
However, it specifically points out their limitation:
they may not detect an intruder who enters by breaking glazing or creating a hole through the door instead of opening it normally.
This is another practical example of layered protection.
A door contact detects one mode of attack.
Other threats may require additional detection or physical protection.
Which external openings should be monitored?
GEBSS says all external doors and external openings accessible by the public should have detectors, including ground-level openings and openings that can be reached by climbing.
This extends the security boundary beyond normal doors.
Potential openings can include:
windows, roof access and other accessible points depending on the building.
The key principle is:
An opening that bypasses the main entrance should not automatically bypass detection as well.
Should intrusion alarm cabling be protected?
Yes.
GEBSS specifically states that cabling for alarm detectors should always be protected.
That is logical because an intrusion system itself can become a target.
An attacker should not be able to defeat detection simply by easily accessing and cutting exposed alarm cabling.
How should CCTV work with intrusion detection?
In its layered-protection section, GEBSS specifically gives CCTV combined with intrusion detection as an example of dual technology that can improve timely and accurate incident detection.
The relationship can be understood as:
Alarm detects → camera helps assess → operator decides → response is initiated.
CCTV is especially useful because it can provide visual context around an alarm.
However, GEBSS separately makes clear that VSS should not be the sole protective measure in an area.
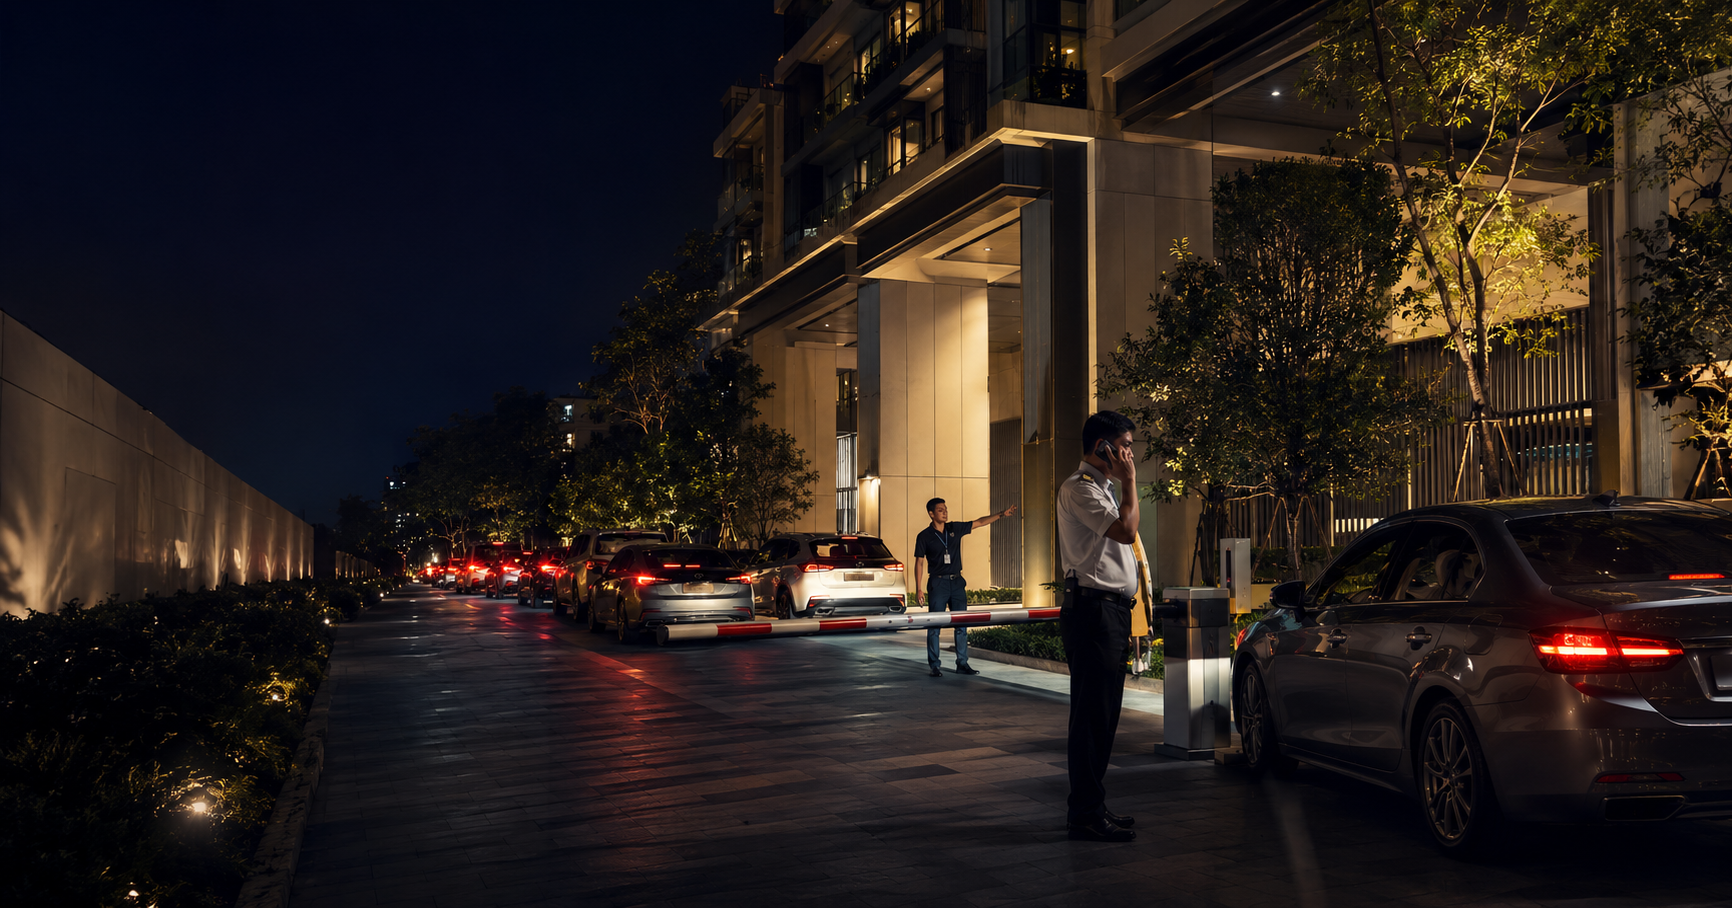
What is a security post?
GEBSS describes a security post as a facility provided where a guard needs to remain at a fixed perimeter or other critical position for extended periods.
Its purpose is to improve the guard’s ability to perform the security role by providing suitable positioning, equipment and protection.
Typical locations can include:
vehicle and pedestrian entrances.
The security post is therefore part of the wider access-control and response arrangement rather than simply a shelter for a guard.
Why does GEBSS treat entrance security posts as important?
The building entrance performs several important functions:
administrative admission, access control and security screening.
GEBSS also notes that an entrance security post may itself become an early target during an attempt to breach the facility.
As a result, the guard post needs to balance:
functionality, aesthetics and protection.
How should a security guard post be positioned?
GEBSS says entrance security posts should provide:
good field of vision and tactical control over the area for which the guard is responsible.
It also recommends suitable lighting and camera coverage, with blind spots avoided where possible and supplemented by CCTV or mirrors where unavoidable.
This is an important design consideration.
A guardhouse can be physically impressive yet operationally poor if:
the guard cannot see approaching vehicles, pedestrians or vulnerable areas.
Should the guardhouse have CCTV?
GEBSS says areas observed by the entrance security post should have proper lighting and camera coverage.
Blind spots should be supplemented with CCTV where they cannot be eliminated.
CCTV in this context supports the guard’s awareness rather than replacing the guard.
Should the main security-system controls be inside the guardhouse?
Generally, GEBSS advises against placing critical building security-system controls in a perimeter or entrance security post, unless the post itself has an adequate protection level.
The reasoning is that an exposed guardhouse can itself be compromised.
GEBSS also says the systems located there should be designed so that the site remains secure if the post is breached.
This is an important distinction between:
an entrance security post
and
the building’s Security Control Room.
Is a guard post the same as a Security Control Room?
No.
They can interact, but GEBSS treats them as distinct functions.
The entrance security post operates at the point where people or vehicles enter and may perform admission, access control and screening.
The Security Control Room is the broader nerve centre for building-security operations.
GEBSS says that where an SCR exists, it should be able to override access-control systems operated from the entrance security post.
That establishes a clear control hierarchy.
Why shouldn’t the guard post provide an easy route into the building?
Because the guardhouse itself may sit at the outer security boundary.
GEBSS says that where the post is exposed to an external threat, the route between the security post and the inner building should be protected.
It also says the entrance to the security post should preferably be from the protected inner side rather than directly from outside.
Where unavoidable connections create a route towards the building, GEBSS says forced-entry protection should be considered to deny or delay the attacker.
Does GEBSS recommend a duress button in the security post?
Yes.
GEBSS says an entrance security post should have a duress button so the guard can alert the security team or local monitoring centre in the event of an attack.
This is a good example of integrating the human security layer with technology.
The guard may be the first person to identify the attack but needs a rapid way to initiate a wider response.
Should the guard post have space for future screening equipment?
Yes.
GEBSS says sufficient space should be provided in the entrance security post for both currently planned and possible future screening equipment.
This ties back to GEBSS’s wider principle of designing buildings so that security can be strengthened when threat levels or requirements change.
How do access control, intrusion detection and guards work together?
Consider an employee entrance.
Access control determines whether the person presenting a credential is authorised.
Door monitoring identifies whether the controlled opening behaves normally.
Intrusion detection can identify abnormal entry or after-hours movement.
CCTV can help assess the event.
The security post or Security Control Room receives information and decides what action is required.
Security personnel provide the human response.
No single component provides the complete security outcome.
How would this work at a Critical Asset room?
Consider a server room.
The access-control system restricts entry to authorised personnel.
The door closer returns the door to the secure position.
A door-position sensor identifies abnormal opening.
Additional intrusion detection may detect other ways of entering the protected area.
CCTV may assist security personnel in assessing the event.
The Security Control Room or other monitoring function receives the alarm.
Security personnel then respond according to procedure.
This is a consultant’s example applying the GEBSS layered-security model. It is not a prescribed universal server-room configuration in the guideline.
Does GEBSS require every server room to have biometric access, CCTV and intrusion detection?
The GEBSS source does not establish that exact universal combination for every server room.
It identifies server rooms as examples of Critical Assets elsewhere in the guideline, and it provides different access-control, detection and protection measures that can be applied according to risk.
The required controls should therefore follow the Risk Assessment and required protection level, rather than simply applying every available technology.
What about after-hours security?
GEBSS explicitly distinguishes between openings used normally during activity hours and those that should be secured during after-hours periods.
Its IDS design includes day/night detectors for doors that may open routinely during the day but should become alarmed when the building transitions to after-hours operation.
This allows the same physical door to operate differently according to the building’s security state.
What are the biggest design mistakes?
A common mistake is treating access control as an IT or reader-installation project rather than a door-security system.
Another is installing alarms without defining what happens when they activate.
Other weaknesses include:
doors that do not self-close, excessive false alarms, unmonitored emergency exits, exposed alarm cabling, blind spots at guardhouses, critical controls placed in an easily compromised post and failure to coordinate security locks with life-safety requirements.
All of these issues reflect a common problem:
The individual security components may work, but the security process does not.
Practical GEBSS Access and Intrusion Review
A building owner or project team can review each important controlled opening using the following questions:
Review Question | What to Check |
|---|---|
What does this door protect? | Area or Critical Asset behind it |
Who should enter? | Authorised user groups |
How is access controlled? | Card, guard or other suitable method |
Does the door return to secure condition? | Automatic closing and locking |
Can unauthorised opening be detected? | Door/opening detector |
Can the opening be bypassed another way? | Glazing, wall, ceiling, adjacent openings |
What changes after hours? | Day/night alarm behaviour |
Can the alarm be clearly located? | Zone and detector identification |
Can the event be assessed? | CCTV / operator awareness where appropriate |
Who receives the alarm? | Security post, SCR or other monitoring function |
What happens next? | Defined response |
Does the design preserve life safety? | Fire and emergency-egress coordination |
This is a consultant’s review structure derived from GEBSS principles rather than a GEBSS-prescribed checklist.
Common misunderstandings
“If a door has a card reader, it is secure.”
Not necessarily. GEBSS treats access control as a combination of hardware, physical elements and procedures.
“Every door in the building needs access control.”
No. GEBSS expects designers to identify the areas and assets that require restricted access.
“A door contact will detect every forced-entry attempt.”
No. GEBSS specifically notes that a magnetic switch may not detect someone entering by breaking through glazing or the door itself.
“More sensitive detectors are always better.”
Not necessarily. GEBSS warns that excessive false alarms can lead to genuine alarms being ignored.
“An emergency exit should be left completely outside the security system.”
No. GEBSS says emergency exits should be monitored for unauthorised opening while still complying with emergency-door regulations.
“The guardhouse should contain all security-system controls.”
GEBSS says critical controls should generally not be located in an exposed entrance or perimeter post unless it has adequate protection.
“The guardhouse and Security Control Room are basically the same thing.”
No. GEBSS envisages the SCR having higher-level control, including the ability to override access controls operated from the entrance post.
Conclusion
GEBSS does not treat access control, intrusion detection and security personnel as separate islands.
They form parts of the same security chain.
Access control decides who should enter.
The physical door enforces the boundary.
Intrusion detection identifies abnormal entry or attempts to bypass the boundary.
CCTV and other information can help assess what is happening.
The security post or Security Control Room receives and manages the event.
Security personnel provide the response.
The strongest design is therefore not necessarily the one with the most card readers or alarm sensors.
It is the one where:
an unauthorised attempt is difficult to carry out, detected early, clearly understood and followed by an effective response before the protected asset is compromised.
From Manpower to Managed Security. One operator, total accountability.
Company
Resources